All topicsCyber security awareness
What is phishing, and why do convincing messages fool people?
Phishing works by borrowing trust from familiar people and everyday tasks. Understanding that mechanism is more useful than hunting for spelling mistakes.
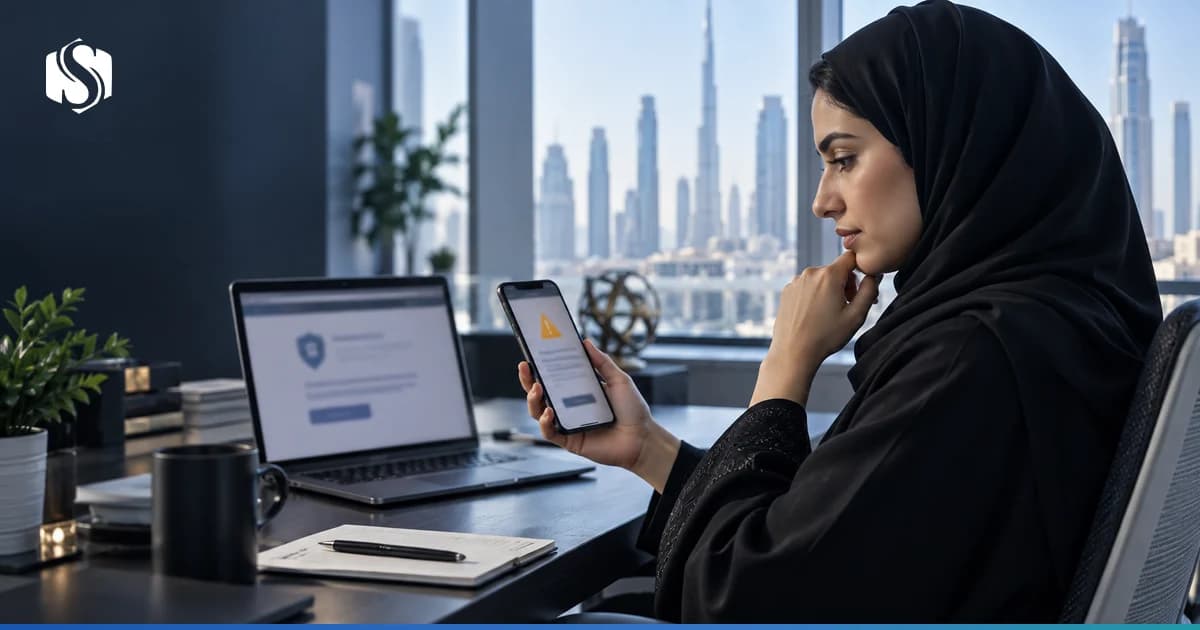
Imagine an employee waiting for a supplier's quotation. An email arrives with a familiar company name and a link to a shared document. The page asks them to sign in. Nothing about the task feels unusual: opening documents is part of the job.
That is the opportunity phishing exploits. It is a form of deception that persuades someone to reveal information, open harmful content or perform an action for an attacker. The message borrows the appearance of something legitimate so that the next step feels reasonable.
The important question is not simply whether an email looks suspicious. It is whether there is a sound reason to trust the action it asks you to take.
Why does phishing work even when people know about it?
Work depends on ordinary acts of trust. Employees open files from colleagues, respond to customers and follow instructions from managers. A phishing message places a harmful request inside one of those familiar routines.
Urgency makes the problem worse. A threat that an account will close today, or a request to pay before a supplier stops work, pushes the recipient towards solving the apparent problem rather than checking whether the problem is real. Authority can have the same effect: people may hesitate to question a message that appears to come from their director.
This does not mean that anyone who responds is careless. A message can arrive at exactly the right moment, use accurate details and come from a genuine account that has been compromised. Prevention needs sensible approval processes and technical protection as well as individual attention.
What happens after the click?
The outcome depends on the attack. A false sign-in page may capture a password. An attachment may attempt to install harmful software. A message may need no malicious link at all: it may simply persuade accounts staff to send money to a different bank account.
Consider a hypothetical supplier-payment exchange. The invoice amount and purchase order are correct, but the sender says the bank details have changed. The accurate details make the conversation credible. They do not establish that the new account belongs to the supplier.
That distinction explains why checking the logo or reading the message twice is not enough. The payment instruction needs confirmation through an established contact route, independent of the message requesting the change.
Phishing, spear phishing, smishing and vishing
These terms describe different forms of the same underlying deception. Spear phishing targets a particular person or business, using details about their role or work. Smishing arrives through text messages. Vishing uses a voice call.
The UAE Cyber Security Council's smishing advisory describes messages impersonating a government service. The authority being imitated changes, but the mechanism is familiar: a trusted name, an apparent problem and a request to act.
Voice or video impersonation can make the request more persuasive still. Our deepfake fraud article explains why recognising a face or voice is not the same as authorising a transaction.
What makes verification independent?
Opening the service through a saved bookmark avoids relying on the supplied link. Calling a supplier on a number already held in approved records avoids relying on a replacement number in the suspicious email. Using the company's normal payment approval keeps the decision separate from the conversation.
By contrast, replying to the same email with “Is this really you?” may reach the attacker again. A padlock in the browser only indicates an encrypted connection; it does not establish that the page represents the organisation you intended to visit.
The amount of checking should fit the action. A request to change bank details or disclose confidential files deserves more scrutiny than an ordinary meeting invitation. Clear rules for sensitive actions reduce the need for every employee to make an improvised security judgement.
Reporting a mistake can prevent a larger one
Clicking a link, entering a password and transferring money are different incidents. Explaining exactly what happened helps the response team decide whether to review the device, secure an account, contain a disclosure or contact a bank.
Speed matters more than embarrassment. If credentials were entered, the genuine account needs securing with IT support, including review of active sessions. If money was sent, finance and the bank need to know promptly. Keeping the original message and transaction details gives them something concrete to investigate.
A workplace that welcomes early reports has a better chance of interrupting the damage. Treating every report as a personal failure gives employees a reason to wait.
Questions we are asked
Short answers on the points readers raise most about this topic.
- I opened a link but did not enter anything. Does that mean I am safe?
- It does not prove that harm occurred, but it does not establish safety either. Tell IT which link you opened and whether anything downloaded or prompted you to approve access. They can assess the device and account based on the actual events.
- Does multifactor authentication stop phishing?
- It reduces account risk, but some methods can still be tricked into accepting codes or approvals, and MFA does not prevent an employee from authorising a fraudulent payment. CISA distinguishes phishing-resistant authentication from weaker methods; your IT team should choose appropriate protection.
Related articles
- AI, data protection and the workplaceAI at work: where useful assistance ends and responsibility begins
- Data protection and privacyUAE data protection at work: what happens to information after you collect it?
- AI-enabled fraud and cyber awarenessDeepfake fraud: when a familiar voice is no longer proof
Train your people, and keep records an inspector can read.